Virtual Private Network (VPN)
Virtual
Private
Network
(VPN)
is
defined
as
network
connectivity
deployed
on
a
shared
infrastructure
with
the
same
policies
and
security
as
a
private
network.
A VPN can be between two end systems, or it can be between two or more networks.
A VPN can be built using tunnels and encryption. VPNs can occur at any layer of the OSI protocol stack.


VPNs provide three critical functions:
Confidentiality (encryption) – The sender can encrypt the packets before transmitting them across a network.
– By doing so, no one can access the communication without permission.
– If intercepted, the communications cannot be read.
Confidentiality (encryption) – The sender can encrypt the packets before transmitting them across a network.
– By doing so, no one can access the communication without permission.
– If intercepted, the communications cannot be read.
Data integrity – The receiver can verify that the data was transmitted through the Internet without being altered.
Origin authentication – The receiver can authenticate the source of the packet, guaranteeing and certifying the source of the information.
VPN Overview:

The primary benefits include:
VPNs offer lower cost than private networks.
– LAN-to-LAN connectivity costs are typically reduced by 20 to 40 percent over domestic leased-line networks.
VPNs offer lower cost than private networks.
– LAN-to-LAN connectivity costs are typically reduced by 20 to 40 percent over domestic leased-line networks.
VPNs offer flexibility for enabling the Internet economy.
– VPNs are inherently more flexible and scalable network architectures than classic WANs.
VPNs offer simplified management burdens compared to owning and operating a private network infrastructure.
VPNs provide tunneled network topologies that reduce management burdens.
– An IP backbone eliminates static permanent virtual circuits (PVCs) associated with connection-oriented protocols such as Frame Relay and ATM.
Encryption Algorithms:
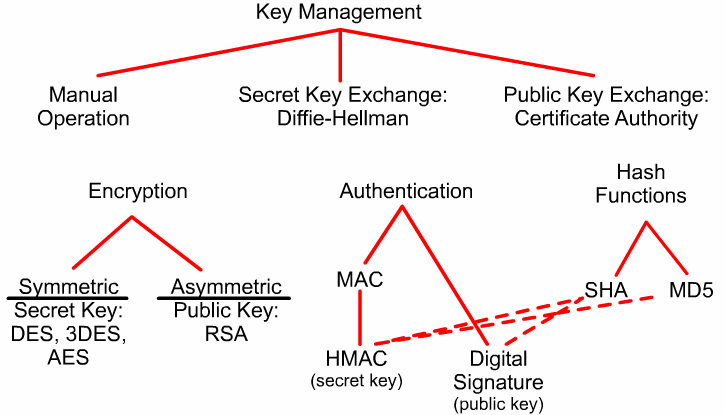
Common Symmetrical algorithms
– 56 bit
Data
Encryption
Standard
(DES)
– 168 bit 3DES, “triple DES”
– 128 or 256 bit Advanced Encryption Standard (AES)
Advantages of Symmetrical algorithms
– Speed, fast
– Mathematical computations are easy to implement in hardware
– Good for large amounts of data
Disadvantage of Symmetrical algorithms
– Sender and receiver share same passwords.
– There is the problem of how to share the password (key management)
Common Asymmetrical algorithms
– RSA, ElGamal, eliptic curves
Advantages of Asymmetrical algorithms
– No problems with key management, one key is kept private and the other key is public and given to anyone that needs to encrypt data.
– Great for authentication because you are the only one with the private key used to decrypt the data.
– Can be used for digital signatures, authenticated key exchanges, email or small amounts of data.
– Based on very hard mathematical equations.
Disadvantage of Asymmetrical algorithms
– Slower in encrypting than symmetrical algorithms
Some qualities to consider in a good encryption algorithm:
– Security against cryptographic attacks
– Scalable, variable length keys
– Any change to the clear-text input should result in a large change to the encrypted output
– No restrictions on import of export


Asymmetrical:
Symmetrical algorithm – A shared key algorithm that is used to encrypt and decrypt a message.
– Use the same key to encrypt and decrypt the message.
– Use the same key to encrypt and decrypt the message.
Asymmetrical algorithm – Uses a pair of keys to secure encrypt and decrypt a message.
– Uses one key to encrypt and a different, but related, key to decrypt.
– Uses one key to encrypt and a different, but related, key to decrypt.
Hashing:
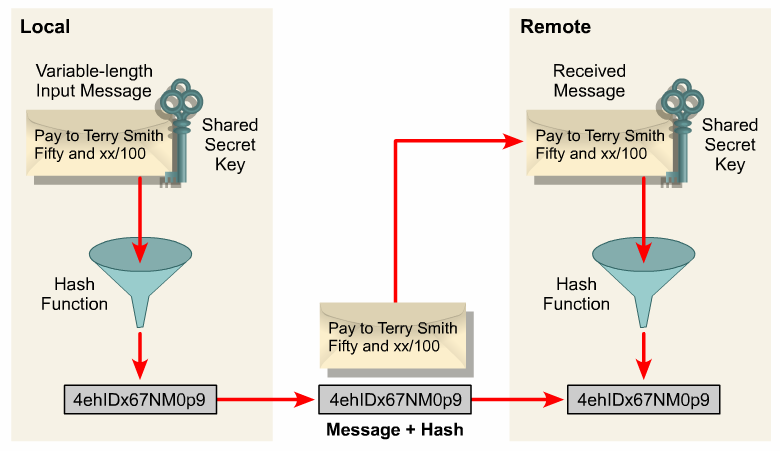
Hashing algorithms is a one-way algorithm that produces a fixed-length output, no matter what the size of the input is.
Analogy:
– Blender with 3 small oranges and 3 big oranges
– Blend it and make one cup of juice
– Your neighbor can do the exact same thing
– You can never reverse-engineer the output to get the input.
– You can’t determine that 3 big and 3 small oranges were used to make the one glass of juice.
Two common hashing algorithms:
– MD5: fixed-length 128 bit output
– SHA-1: fixed-length 160 bit output (preferred, less likely to result in a collision two different inputs giving the same output).
Qualities in a good hashing algorithm:
– High resistance to cryptographic attack
– Any change to the clear-text input results in a large change in the encrypted output.
– The probability of collision is low.

No comments:
Post a Comment
Note: only a member of this blog may post a comment.